Key Takeaways
- The $93.4M Ledger hardware wallet exploit has allegedly expanded to Mediamarkt, a major European retailer.
- A customer found an earlier implant version that passes software checks, warning others to inspect devices.
- Ledger claims the attack is limited to Asian reseller CryptoBilis but is now reviewing reseller controls.
New Tampered Ledger Wallets Allegedly Found Outside Asia
While the investigation into the recent $93.4M exploit that hit Ledger wallets sold in Asia by CryptoBilis, an authorized Ledger reseller, progresses, reports link the exploit to additional resellers in other regions.
Ledger has only acknowledged that a hidden implant was present in one of the devices affected by the million-dollar theft. Nonetheless, X user Johannes (4, 4) has presented evidence of more implants in another Ledger wallet reportedly purchased from Mediamarkt, a German chain of stores with a presence in several European countries, including Italy, Spain, Turkey, Poland, Austria, and the Netherlands, among others.
Johannes (4, 4), who allegedly acquired this wallet two weeks ago, pointed out that this implant seemed to be an earlier version, as it fails to hide the implant behind the device screen to make its detection difficult. Nonetheless, he explained that his wallet, while compromised, did not transfer his funds to the exploiter. “Either the device didn’t work, or they were waiting for a more widespread usage of the compromised devices,” he speculated.
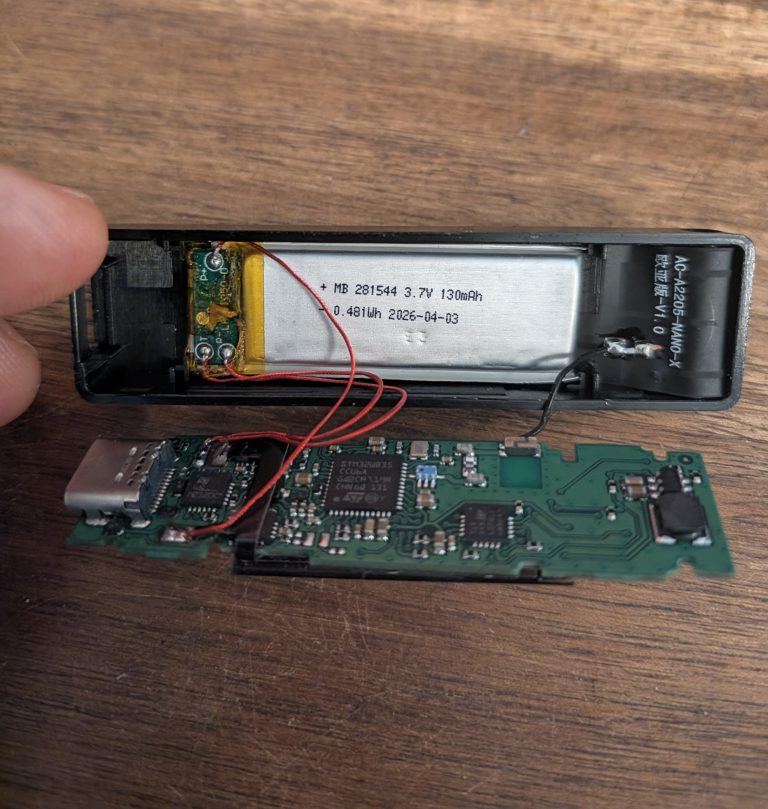
Former Mt Gox CEO Mark Karpeles added that the antenna in this wallet read “Eurasian version,” hinting at different versions depending on the mobile frequencies used in each region.
Before, Mark Karpeles documented similar implants present in wallets sourced from Malaysia, where Cryptobilis is based. This new report expands the exploit to wallets offered in Europe, potentially exposing more customers to this attack vector.
Finally, Johannes (4, 4) recommended that Ledger owners who sourced their wallets from resellers open their devices and not trust Ledger’s software checks, as similar cases have appeared in other regions. All tampered devices passed Ledger software security checks, prompting customers to use them without concerns.
In its most recent update, Ledger clarified that all confirmed cases affected by this exploit were limited to devices sold through CryptoBilis, encouraging affected users to “reach out to Ledger Support through official channels and file complaints with their local law enforcement authorities.”
“We are continuously improving that work now and events like this strengthen our resolution: reviewing authorized reseller controls, advancing hardware protections, and cooperating with authorities,” Ledger concluded.
At the time of writing, Ledger Support has not addressed the swirling reports concerning alleged tampered devices stemming from European resellers.